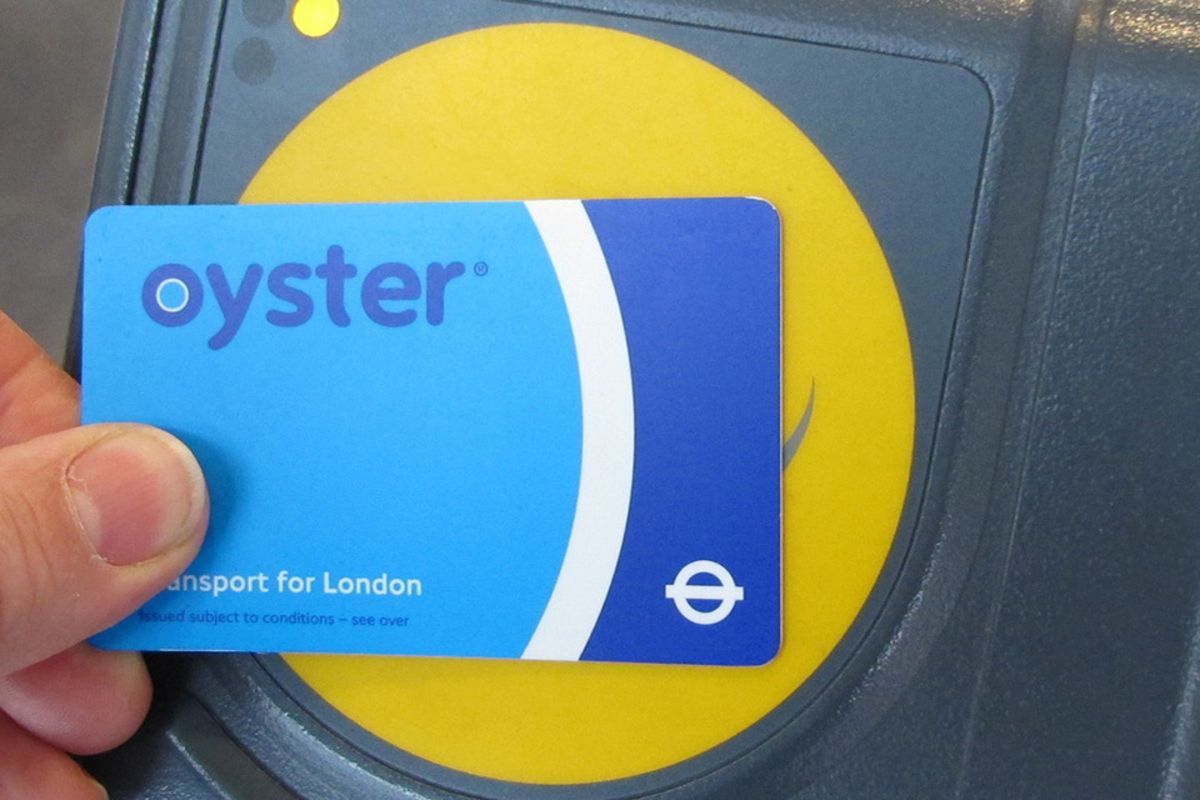
London’s transport authority, Transport for London (TfL), has confirmed a significant data breach affecting 265,000 users of its Oyster photocard system. Hackers gained unauthorized access to the system, compromising sensitive personal information of individuals who use these specialized travel cards.
What Happened?
The security incident came to light when some account holders received official emails requesting them to re-register their accounts. This anomaly suggested that the attackers might have directly used TfL’s official systems to send fraudulent communications, rather than simply spoofing sender addresses.
In response to the breach, TfL immediately took the Oyster photocard website offline to prevent further unauthorized access and began an investigation into the matter.
Who Was Affected?
The compromised data pertains to users of specific Oyster photocard types, including:
- Zip Oyster cards (for ages 5-10, 11-15, and 16+)
- 18+ Student Oyster cards
- 18-25 Care Leaver Oyster photocard holders
- 60+ Londoner Oyster photocard holders
- Veterans Oyster photocard holders
- Apprentice Oyster photocard holders
Oyster photocard is a type of named travel card used within London’s public transport network. It is typically used by eligible residents such as seniors, veterans, children, students, apprentices, and young people leaving care, who are entitled to free or discounted travel.
Unlike regular, anonymous Oyster cards, Oyster photocard requires users to provide personal details, including their name, address, date of birth, and a photograph for verification.
What Data Was NOT Compromised?
TfL has clarified that certain sensitive information remains secure. The breach did not impact:
- Names and dates of birth of children holding Zip Oyster cards.
- User passwords.
- Bank account or payment card details.
- Travel history.
- Photographs from the photocards themselves.
TfL’s Response and User Actions
Shashi Verma, TfL’s Chief Technology Officer, stated that the security incident has been contained. “We have a high degree of confidence that the number of people affected has been significantly reduced due to our swift action in identifying and dealing with this incident,” Verma said. “We are continuing to investigate the exact circumstances, but we have contacted those users who we believe may be affected to inform them of the situation.”
TfL has also reported the incident to the UK’s Information Commissioner’s Office (ICO), the independent body responsible for upholding information rights in the UK.
As a precautionary measure, TfL is urging all Oyster photocard users to change their account passwords and security questions and answers. Furthermore, users are strongly advised to update their passwords on any other websites or online services where they may have used the same credentials, to mitigate the risk of further unauthorized access to their accounts.