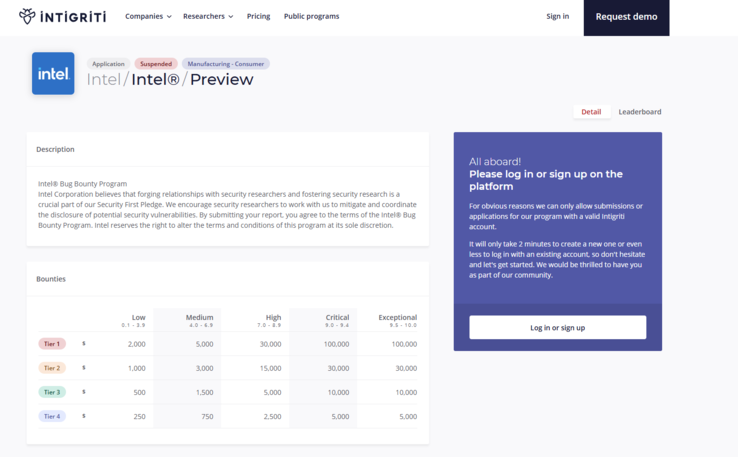
In a surprising move that has sent ripples through the cybersecurity community, Intel has abruptly discontinued its long-standing bug bounty program. The tech giant has transitioned to a new vulnerability reporting system hosted on the Intigriti platform, which notably omits any form of cash compensation for researchers.
Shift Away From Monetary Incentives
Previously, Intel’s program offered substantial rewards, with top payouts reaching up to $100,000 USD for the discovery of critical security flaws. However, the newly established project on Intigriti is explicitly labeled as a “responsible disclosure” initiative, signaling a definitive end to monetary rewards for vulnerability submissions.
While researchers can still report vulnerabilities found in Intel’s hardware, firmware, software, and open-source projects, these discoveries will no longer be met with financial incentives. The original bug bounty program, initially launched in 2017 as an invite-only program and opened to all security researchers in 2018, was instrumental in identifying and rectifying high-risk defects before malicious actors could exploit them. In 2020 alone, nearly half of the Common Vulnerabilities and Exposures (CVEs) patched by Intel originated from this bounty program.
The reward structure was tiered, with minor vulnerabilities earning researchers $250 USD and the most severe issues potentially netting the maximum $100,000 USD. This sudden halt comes as a surprise, especially considering Intel’s public statements in early 2025 about evaluating and optimizing its bug bounty criteria.
The AI Influence?
Intel has not yet provided an official explanation for this abrupt change. However, emerging trends in the cybersecurity landscape suggest that the rise of artificial intelligence could be a significant contributing factor. Recently, various open-source projects have been inundated with security reports automatically generated by AI tools.
The number of CVEs associated with each Linux kernel version has reportedly surged from approximately 500 to nearly 2,000, overwhelming maintainers. Linus Torvalds, the founder of Linux, recently commented on how a deluge of repetitive, AI-generated reports has nearly paralyzed the management of security advisories.
This situation mirrors challenges faced by other projects. The open-source project Curl, for instance, had to suspend its own bug bounty program due to an overwhelming influx of low-quality, automated submissions. Similarly, HackerOne’s Internet Bug Bounty program paused submissions earlier this year, citing the rapid proliferation of AI-assisted vulnerability hunting as the cause for a surge in reports that has crippled existing processing systems.
Intel’s Potential Strategy
It is highly probable that Intel is experiencing a similar issue with a massive influx of AI-generated vulnerability reports. By eliminating cash incentives, the company may be attempting to manage the sheer volume of submissions, prioritizing quality and relevance over quantity.
As it stands, security researchers analyzing Intel products will no longer receive financial rewards for their findings submitted through the new system.